Leon Lorenz · 5 October 2026
Examining Adaptive Camouflage Strategies for Virtual Perimeter Defenses in Cloud Environments
Cloud environments have expanded rapidly since the early 2020s, and virtual perimeter defenses now rely on adaptive camouflage strategies that shift resources and obscure boundaries in real time. These methods combine moving target defense principles with machine learning models that monitor traffic patterns and adjust visibility thresholds accordingly. Researchers at institutions across North America and Europe have documented how such techniques reduce the attack surface by altering IP allocations, port assignments, and service endpoints at intervals measured in seconds rather than hours.
Core Components of Virtual Perimeter Defense
Virtual perimeters in cloud setups differ from traditional network boundaries because they lack fixed hardware locations, which means defenses must operate through software-defined controls that span multiple availability zones. Adaptive camouflage builds on this foundation by introducing variability in response to detected reconnaissance attempts, and data from cloud service providers indicates that organizations implementing these layers see measurable drops in successful enumeration scans. Studies conducted through 2025 show that systems employing dynamic obfuscation handle distributed denial-of-service probes more effectively when camouflage layers rotate encryption keys and routing tables simultaneously.
One approach involves polymorphic routing tables that change topology based on behavioral analytics engines, while another uses decoy instances that mimic production workloads to draw automated scanning tools away from actual assets. Those who have analyzed large-scale cloud deployments note that combining these elements creates overlapping uncertainty zones that complicate lateral movement for adversaries.
Techniques Driving Adaptive Camouflage
Adaptive camouflage strategies typically integrate several coordinated mechanisms. Traffic morphing alters packet signatures to resemble benign application flows, and this occurs alongside workload migration that relocates containerized services across regions without interrupting availability. Artificial intelligence models trained on historical threat data predict likely probe vectors and trigger preemptive camouflage adjustments, according to findings published by the National Institute of Standards and Technology in its cloud security frameworks.
Another layer involves micro-segmentation enhanced with time-based access tokens that expire and regenerate automatically. Observers tracking adoption rates across industries report that firms in finance and healthcare sectors have incorporated these token systems into their zero-trust architectures by mid-decade. The result is a perimeter that presents different profiles to different observers depending on the context of the connection attempt.
Implementation Patterns Observed Through 2026
By October 2026, major cloud platforms had released updated toolkits that embed camouflage controls directly into orchestration layers, allowing teams to define policies that adapt based on threat intelligence feeds from multiple continents. European Union Agency for Cybersecurity reports highlight how organizations in the region integrated these controls with regulatory compliance requirements, producing audit logs that demonstrate consistent rotation of virtual endpoints. Australian research groups have similarly published datasets showing reduced dwell times for detected intrusions when camouflage mechanisms activate within the first few seconds of anomalous activity.
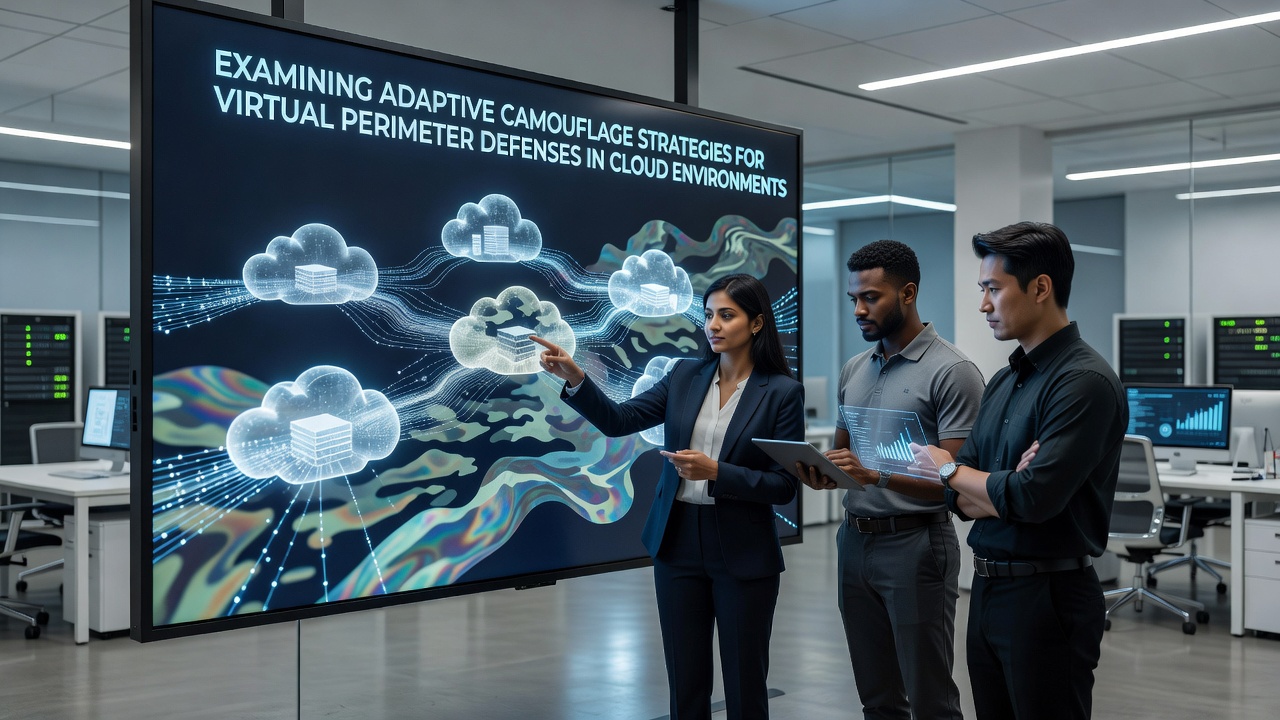
Implementation often begins with baseline mapping of existing traffic, followed by phased introduction of variability controls that avoid disrupting legitimate user sessions. Teams frequently test these configurations in isolated staging environments before rolling them into production, and the process includes continuous feedback loops that refine camouflage parameters using reinforcement learning techniques.
Integration Challenges and Measurement Approaches
Deploying adaptive camouflage requires careful coordination between security operations and development teams because changes to routing or encryption behaviors can affect application performance metrics. Metrics collected by independent testing organizations reveal that properly tuned systems maintain latency within acceptable ranges while still achieving the desired reduction in detectable signals. Challenges arise primarily when legacy applications lack the flexibility to handle frequent endpoint changes, prompting architects to introduce proxy layers that absorb the variability on behalf of older codebases.
Measurement typically focuses on metrics such as time-to-detection for simulated attacks and the volume of reconnaissance traffic that fails to map accurate infrastructure diagrams. Industry reports compiled through collaborative efforts between universities in Canada and Singapore indicate that environments using full adaptive suites experience up to 70 percent fewer confirmed footholds during red-team exercises compared with static configurations.
Conclusion
Adaptive camouflage strategies continue to evolve alongside cloud infrastructure advancements, providing virtual perimeter defenses with the capacity to respond dynamically to emerging threats. The combination of moving target principles, machine learning prediction, and automated rotation mechanisms creates layered uncertainty that strengthens overall resilience. As platforms release further tooling updates and regional agencies publish additional guidance, organizations gain clearer pathways for integrating these approaches into existing security programs while maintaining operational continuity.